Software development, information security and ISO certification support — New Delhi
contact@isoftapplications.com
Software development & information security, New Delhi

Software your institution runs on. Security it can certify.

We design and build web applications, portals and management systems for universities, hospitals, government bodies and businesses, then help you secure them and take them through ISO/IEC 27001 and ISO 9001 certification.
Team members working together at laptops in a bright office
ISO/IEC 27001:2022Implementation & audit support
300+web applications delivered
ISO 27001& ISO 9001 certification support
End to endbuild, host, secure and support

Trusted by universities, hospitals and organisations in India and abroad
  • National Law University Delhi
  • National Law Institute University Bhopal
  • Delhi Metro Rail Corporation
  • American Cancer Society
  • Centers for Disease Control and Prevention
  • University of Washington
  • Anand Automotive
  • Simplot
  • Wilbur-Ellis
  • Shree Hospital, Dwarka
  • Pinkathon
  • NISHK
Digital Personal Data Protection Act, 2023 & DPDP Rules, 2025

Is your organisation ready for the DPDP Act?

India’s first comprehensive data protection law applies to every organisation that collects or processes personal data in digital form — universities, hospitals, companies, NGOs and government bodies alike. The Rules were notified on 13 November 2025, and the main obligations become enforceable on 13 May 2027.

We help you put the Act into daily practice: mapping your personal data, fixing notices and consent, handling rights requests and breaches, and keeping the evidence an inquiry by the Data Protection Board would ask for — all managed in our own compliance platform, DPDP360.

  1. 11 Aug 2023Act passedDPDP Act, 2023 receives Presidential assent
  2. 13 Nov 2025Rules notifiedData Protection Board of India is constituted
  3. 13 Nov 2026Consent managersRegistration and obligations of consent managers begin
  4. 13 May 2027Full complianceNotice, consent, security, breach, retention and rights duties apply

What the Act requires of a data fiduciary

  • Notice & consentClear, itemised notice and free, specific, unambiguous consent for each purpose — and withdrawal as easy as giving it.
  • Rights of data principalsAccess, correction, erasure, nomination and grievance redressal, with published procedures and timelines.
  • Security safeguardsReasonable measures such as encryption, access control, logging and backups to prevent a personal data breach.
  • Breach notificationInform the Data Protection Board and affected people without delay, with a detailed report to the Board within 72 hours.
  • Retention & erasureDelete data once its purpose is served or consent is withdrawn, while keeping the logs the Rules require for one year.
  • Children’s dataVerifiable parental consent before processing the data of anyone under 18, and no tracking or targeted advertising.
  • Significant data fiduciariesA Data Protection Officer in India, an independent data auditor, and an annual Data Protection Impact Assessment.
  • Processors & vendorsContracts that bind every processor handling personal data on your behalf to the same standards.

Up to ₹250 crore penalty for a single instance of failing to take reasonable security safeguards; up to ₹200 crore for failing to notify a breach or meet obligations on children’s data.
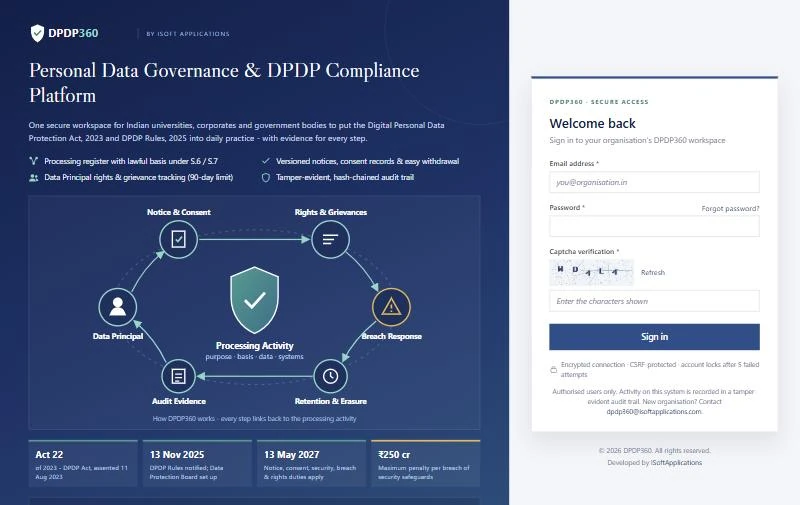
DPDP360 sign-in page showing the personal data governance cycle: notice and consent, rights and grievances, breach response, retention and erasure, and audit evidence

DPDP360 compliance platform

One secure workspace for universities, companies and government bodies to run DPDP compliance every day, with evidence for every step.

  • Processing register with lawful basis under Sections 6 and 7
  • Versioned notices, consent records and one-click withdrawal
  • Data principal rights and grievance tracking within the 90-day limit
  • Breach response workflow with Board and individual notifications
  • Retention schedules and erasure with proof of deletion
  • Tamper-evident, hash-chained audit trail

How we implement the DPDP Act in your organisation

  1. Discover

    Map every system, form and vendor that touches personal data.

  2. Assess

    Gap assessment against the Act and Rules, with a prioritised plan.

  3. Fix

    Notices, consent flows, privacy policy, contracts and internal procedures.

  4. Deploy

    Set up DPDP360 with your data, roles and workflows.

  5. Train

    Staff awareness, plus breach and rights-request drills.

  6. Sustain

    Periodic audits, monitoring and support as the rules evolve.

Full enforcement begins on 13 May 2027. Start with a DPDP readiness assessment and know exactly where you stand.

What we do

Three practices, one team accountable for the whole system

Most organisations hire one firm to build software and another to secure it. We do both, so nothing falls between contracts.

Developer working on a laptop in the office

Build

Custom web and mobile applications, built to fit how your organisation actually works.
  • Web portals and management systems
  • Mobile apps for Android and iOS
  • E-learning and LMS platforms
  • WordPress, Drupal and Joomla sites
Software development services
Laptop and notebook on a desk during a review session

Secure

Security operations that detect problems early and respond to them on a defined playbook.
  • SOC monitoring and incident response
  • Vulnerability assessment of web apps
  • Hardened hosting and backups
  • Annual maintenance and security AMC
Security operations
Consultant reviewing work with a colleague at her laptop

Certify

We prepare your organisation for certification audits and stay with you through them.

  • ISO/IEC 27001:2022 ISMS
  • ISO 9001:2015 quality management
  • Risk assessment and Statement of Applicability
  • Internal audits and audit-day support
ISO certification support
Illustration of the ISoftRx hospital dashboard app.isoftrx.com ISoftRx Dashboard PatientsAppointmentsPrescriptionsVaccinationsPharmacyReports Good morning, Dr. Mehta Wednesday clinic summary Patients today 48 Vaccinations due 12 Prescriptions 63 Visits this week MTWTFSS Next patients A. Sharma10:15 R. Verma10:30 P. Iyer10:45 S. Khan11:00 New registration
Our products

Ready-made systems, adapted to you

Alongside custom work, we maintain our own management software, deployed and configured to your workflows.

Smart agriculture · United States

IoT and satellite intelligence for US agriculture

We have designed and delivered IoT-based agricultural solutions for the US farming sector, combining field sensors, satellite imagery and data platforms to help growers act earlier and use resources more precisely.
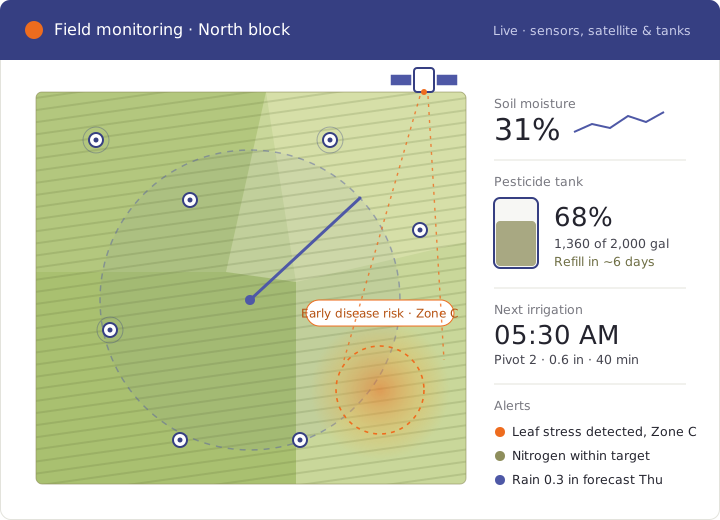
Illustration of a field monitoring dashboard showing soil sensors, a centre-pivot irrigation zone, a satellite-detected disease hotspot, pesticide tank level and irrigation schedule
Sensors, satellite imagery and tank data brought together in one field view.
  1. 01

    IoT-based smart agriculture

    Sensor-based crop monitoring and crop modelling that improve productivity and the efficient use of water, fertiliser and labour.

  2. 02

    Early-stage crop disease detection

    Satellite imagery analysis and remote sensing that flag crop disease early, with actionable insights delivered to farmers.

  3. 03

    Fertiliser & pesticide management

    Smart monitoring and optimisation systems that help farmers apply fertilisers and pesticides precisely and efficiently.

  4. 04

    Tank-based sensor systems

    IoT-enabled sensors that monitor tank levels and manage pesticide storage and usage, with alerts before supplies run low.

  5. 05

    Precision irrigation systems

    Sensor-based irrigation that monitors water levels, optimises irrigation schedules and manages pesticide concentrations where applicable.

Simplot Wilbur-Ellis
In use in the United States

Our tank level monitoring system is used by Simplot and Wilbur-Ellis, US agribusinesses that supply fertilisers and crop protection products, to monitor fertiliser and pesticide tank levels, storage and usage.

  • IoT sensor networks
  • Satellite imaging
  • Remote sensing
  • Crop modelling
  • Precision agriculture
  • Smart irrigation
  • Tank & storage monitoring
  • Dashboards & alerts
Clients & sectors

Who we work with

What our clients share is a need for software that is dependable, auditable and easy for non-technical staff to use.

Universities & education

Recruitment portals, admissions, faculty pages, journals and learning platforms.

Healthcare

Hospital and clinic management, prescriptions, vaccination tracking and pharmacy.

Government & public bodies

Secure citizen-facing portals, hosting, AMC and compliance documentation.

Manufacturing & automotive

Vendor management, procurement workflows and internal operations systems.

Non-profits

Campaign and event sites, donor and volunteer management, content platforms.

Agriculture (USA)

IoT sensing, satellite crop monitoring, precision irrigation and tank management.
Team members reviewing project notes at a laptop
One accountable team

Build · Host · Secure · Support

Why clients stay with us

web applications built and deployed for clients in India and abroad

From single-purpose portals to systems that run a whole institution, each one designed, tested and supported by the same team.

  • A named project lead

    One person accountable from the first meeting to go-live.

  • Working builds early

    You see working software every iteration, not just at the end.

  • Secure by design

    Security controls planned in from day one, not bolted on.

  • Support after launch

    Annual maintenance so the system keeps working for years.

Our method

How a project runs

Every engagement follows the same six stages, with a working build in your hands early and a named contact throughout.

  1. Discover

    We listen, map your workflows and agree what success looks like.

  2. Design

    Screens, data model and architecture, signed off before we write code.

  3. Build

    Short iterations with a demo at the end of each one.

  4. Test

    Functional, security and device testing across browsers and phones.

  5. Launch

    Deployment, data migration and training for your staff.

  6. Support

    Maintenance, monitoring and improvements under an AMC.

Security & compliance

Security is part of the build, not an add-on

Applications we build are designed against the ISO/IEC 27001:2022 control set from day one, which makes the eventual audit far shorter.

INFORMATION SECURITY · ISO/IEC 27001 · 27001 2022 QUALITY MANAGEMENT · ISO 9001 · 9001 2015 MONITOR · DETECT · RESPOND · SOC

Tell us what you need built or certified

Send a short description. We reply within one working day with questions or a first estimate.